Think Cybersecurity Is Just IT’s Job? Think Again.
Think Cybersecurity Is Just IT’s Job? Think Again.
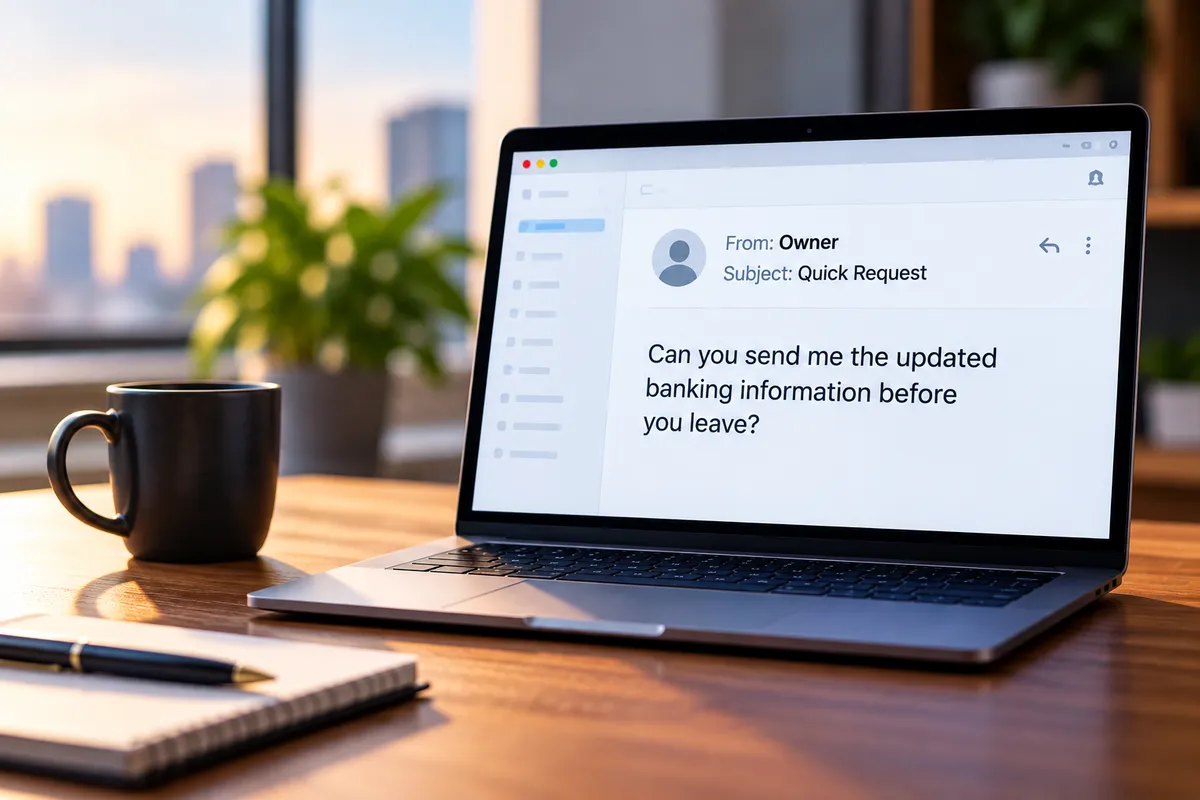
It’s 4:17 on a Friday afternoon. An employee gets an email that looks like it’s from the company owner: “Can you send me the updated banking information before you leave?” The name matches, the tone feels familiar, and with everyone rushing to finish before the weekend, replying seems easiest.
But there’s a problem: the owner didn’t send the email.
Your IT team can set up strong security, watch for suspicious activity, and block many threats before employees see them. But technology can’t make every decision. Sometimes, the difference between catching a suspicious email and facing a real security problem depends on whether an employee knows what to do when something unexpected shows up.
That’s why cybersecurity isn’t just IT’s job. It’s something everyone in the business shares.
Cybersecurity Happens Outside the IT Department
When business leaders think of cybersecurity, they often picture firewalls, antivirus software, security updates, and someone watching the network. Those tools are important. But cybersecurity also happens in daily conversations, emails, financial transactions, and decisions that aren’t only about technology.
Consider how this plays out across industries. At a financial firm, someone might get a request to change a client’s payment instructions. In healthcare, an employee could be asked to send patient records to an unknown address. A manufacturer or aerospace company might get a sudden request for sensitive designs or documents. An accounting firm could receive an email that looks like it’s from a long-term client asking for confidential information.
Different businesses handle different information, but the same question comes up: How does an employee know if a request is real? This is where cybersecurity goes beyond simply technical tools. It becomes part of how your organization makes decisions.
Good Security Tools Can’t Make Every Judgment Call
A well-run IT setup can stop many cyberthreats before they reach employees. Email filters can spot suspicious messages. Multifactor authentication makes it harder for outsiders to get in. Security monitoring can catch unusual activity. But none of these tools replace the need for good judgment.
Cybercriminals can impersonate people you know, reference real business relationships, and send messages that look like normal work requests. Imagine getting an email from a vendor you’ve worked with for years. Everything seems fine, except they give you new banking details and ask you to use them for the next payment.
Is the request real? Maybe. But if an employee approves the change just because the message looks familiar, the business is guessing instead of checking. It’s safer to contact the vendor using a phone number or channel you already trust and confirm the change. That difference is important.
Employees don’t need to be experts at spotting every scam. They need a reliable process for handling risky requests.
“Be Careful” Isn’t a Cybersecurity Procedure
Most employees have heard some version of the advice: “Watch out for suspicious emails.”
That’s good advice, but it doesn’t explain what to do if you get a suspicious email. Should you delete it, forward it to IT, call the sender, or tell your manager? What if you already clicked a link? If these steps aren’t clear, employees must make tough choices under pressure. A practical cybersecurity process should clear up this confusion by covering five key situations.
1. When Something Looks Suspicious
Employees should know exactly where to report a strange email, an unexpected login alert, or a suspicious request. This could mean using a phishing-report button, contacting your IT team, or calling your IT provider. Whatever method you use, it should be simple and easy to use.
2. When Someone Requests Sensitive Information or Changes
Requests about payments, banking details, account access, or confidential records should always follow a set verification process. For example, if someone gets new payment instructions, they should confirm the change using contact details the company already trusts.
Don’t use contact details from the suspicious request to verify it.
3. When an Employee Isn’t Sure What to Do
Employees should feel okay about stopping to ask for help. This might seem simple, but workplace pressure can make people hesitate to question a boss, interrupt a manager, or delay a task. A good process lets employees slow down if anything feels wrong.
4. When Someone Has Already Made a Mistake
This is especially important. If an employee clicks a suspicious link, opens a strange attachment, or types their password into a fake website, they might feel embarrassed or hope nothing happens. They might wait and see, but waiting can make things worse.
Employees should report the problem right away, even if they’re not sure anything bad happened. Then IT or the security team can decide what to do next, like securing an account, checking the device, or stopping suspicious activity.
Employees don’t need to figure out the problem themselves. They need to know how to report it.
5. When the Request Comes From Someone Important
Security procedures need to apply to everyone, including executives. If a company requires verification for unusual payment requests, that requirement shouldn’t disappear because the message appears to come from the owner. In fact, impersonating someone in authority is one way attackers pressure employees into skipping normal procedures.
A clear process protects employees by giving them a reason to verify a request without making it personal.
Leadership Sets the Standard for Cybersecurity Culture
Here’s something businesses sometimes overlook. Employees don’t learn what’s important only from written policies. They learn from watching how leadership behaves.
If an executive often skips security steps because they’re busy, employees might start thinking those steps are optional. If managers react badly when someone asks about a strange request, employees may stop speaking up. If someone is embarrassed in front of others for a security mistake, the next person might not report one. That hesitation can be risky.
The faster IT or security hears about a problem, the faster they can respond. But employees are less likely to report issues quickly if they think they’ll get in trouble just for speaking up.
A good cybersecurity culture allows for honest mistakes but still expects everyone to follow the rules. It also recognizes employees who make smart security choices. When someone checks an unusual request, they’re not being difficult; they’re protecting the company.
When an employee reports a suspicious email, they’re not wasting IT’s time. They’re helping the business check out a possible threat.
Cybersecurity becomes part of your culture when leaders treat responsible security actions as smart business, not as a hassle.
What Does Shared Cybersecurity Responsibility Look Like?
Let’s go back to Friday afternoon at 4:17. An employee gets what looks like an urgent request from the owner. Instead of replying right away, they notice the request is about sensitive financial details.
They follow the company’s process to check the request. They contact the right person using a trusted method, find out the owner didn’t send the email, and report the suspicious message to IT.
There’s no big confrontation or complicated investigation. The employee just follows a familiar process at the right time. That simple step may have stopped financial loss, account problems, or leaks of sensitive information.
That’s what shared cybersecurity responsibility looks like in real life. IT sets up technical protection and handles incidents. Leadership sets expectations and supports employees who follow them. Employees know when to be careful, check sensitive requests, and report concerns quickly.
Each group has its own role, but together they all help protect the business.
Five Questions Every Leadership Team Should Ask
You don’t have to wait for a cybersecurity problem to see if your employees know their responsibilities. At your next leadership or IT meeting, ask these questions:
1. Do employees know exactly how to report suspicious activity?
It’s not enough to know they should report it; they need to know who to contact and how.
2. Do we have a consistent process for verifying sensitive requests?
This is especially important for changes concerning payments, account access, or confidential information.
3. Does everyone know what to do if they accidentally click something suspicious?
Employees should know that reporting quickly is more important than trying to hide or fix a mistake by themselves.
4. Does leadership follow the same security procedures as everyone else?
If the rules change based on who’s making the request, employees might not know when they need to verify something.
5. Do employees feel comfortable bringing up concerns?
A reporting process only works if people feel comfortable using it.
Try this exercise: Ask a leader, someone from IT, and an employee outside IT how they would handle the same suspicious request. If their answers are different, you’ve found a good place to improve your procedures.
Your IT team or IT provider can help set up technical protection, reporting channels, and response steps. But leadership also needs to make sure everyone understands, supports, and follows these procedures.
Cybersecurity Isn’t Just an IT Job. It’s How Your Business Operates.
Cybersecurity isn’t just about blocking bad software or protecting the network. It’s also about the choices people make every day at work, like handling an unexpected payment request, a suspicious attachment, an unusual login alert, or a message that seems to come from someone important.
These situations aren’t always security threats. That’s why businesses need more than just good technology. They need clear steps, supportive leaders, and employees who know when to pause, check, and report.
The goal isn’t to make everyone a cybersecurity expert. It’s to make sure everyone knows their part in keeping the organization safe. So, the next time a strange email shows up at 4:17 on a Friday, your team won’t have to guess what to do.
They should already know the right steps.